
I would like to wish everyone a Merry Christmas, Happy Hanukkah, Happy Kwanzaa, etc… and a Happy New Year. 🙂
Regards,
Roger Lacroix
Capitalware Inc.
I would like to wish everyone a Merry Christmas, Happy Hanukkah, Happy Kwanzaa, etc… and a Happy New Year. 🙂
Regards,
Roger Lacroix
Capitalware Inc.
Mike Hadlow has posted an excellent blog item that every IT Manager should (must) read:
http://mikehadlow.blogspot.co.uk/2013/12/are-your-programmers-working-hard-or.html
Regards,
Roger Lacroix
Capitalware Inc.
At first I thought this article ‘Over-Engineering the Perfect Mug of Coffee‘ at Slashdot was a joke but it is real. Since coffee fuels my programming, I’m seriously thinking of getting one through the KickStarter project or maybe I’ll ask Santa for it. 🙂
The company that will be creating the mugs is called Joevo. The KickStarter project for the ‘The Temperfect Mug‘ can found here.
Regards,
Roger Lacroix
Capitalware Inc.
As I mentioned in this blog posting, I use a UFM Workflow to perform a daily backup of selected directories, encrypt the compressed files then upload the encrypted files to a remote server.
In this blog posting, I will show you how to create a UFM Workflow that will compress the contents of 3 directories (and sub-directories), encrypt the 3 zip files and then use Sftp to upload the 3 files to a remote server. This example is designed for a Windows desktop PC but it could easily be modified for Linux, Mac OS X, Unix, etc.
Step #1: On the Windows PC in the UFM install directory, create a file called ufm_zip_enc_ftp.xml and copy the following into the file:
<?xml version="1.0" encoding="ISO-8859-1"?>
<!DOCTYPE UFM_Workflow SYSTEM "UFM_Workflow.dtd">
<UFM_Workflow>
  <Global>
    <Property name="UploadDir" value="G:\Upload" />
  </Global>

  <Actions>
    <Delete>
      <File dir="${UploadDir}">*</File>
    </Delete>

    <Zip todir="${UploadDir}" tofile="data.zip">
      <File>E:\Data</File>
    </Zip>

    <Zip todir="${UploadDir}" tofile="eclipse_wk.zip">
      <File>F:\eclipse\workspace</File>
    </Zip>

    <Zip todir="${UploadDir}" tofile="VSData.zip">
      <File>F:\VSData</File>
    </Zip>

    <EncryptFile todir="${UploadDir}"
              tofile="data.enc"
              keysize="256"
              passphrase="decrypt_this_NSA..1..can't_touch_this!!">
      <File>${UploadDir}\data.zip</File>
    </EncryptFile>

    <EncryptFile todir="${UploadDir}"
              tofile="eclipse_wk.enc"
              keysize="256"
              passphrase="decrypt_this_NSA..2..can't_touch_this!!">
      <File>${UploadDir}\eclipse_wk.zip</File>
    </EncryptFile>

    <EncryptFile todir="${UploadDir}"
              tofile="VSData.enc"
              keysize="256"
              passphrase="decrypt_this_NSA..3..can't_touch_this!!">
      <File>${UploadDir}\VSData.zip</File>
    </EncryptFile>

    <SFtp xmlfile="sftp_upload.xml" />

  </Actions>
</UFM_Workflow>
So lets review the 8 actions in the UFM Workflow.
Step #2: On the Windows PC, in the sftp directory, create a file called sftp_upload.xml and copy the following into the file:
<?xml version="1.0" encoding="ISO-8859-1"?>
<!DOCTYPE UFM_SFtp SYSTEM "UFM_SFtp.dtd">
<UFM_SFtp>

  <Hostname>10.10.10.10</Hostname>
  <UserID>MyUserID</UserID>
  <Password>mypwd</Password>

  <SFtpCmds>

    <Put remotedir="secureDir">
      <File dir="G:\Upload">*.enc</File>
    </Put>

  </SFtpCmds>

</UFM_SFtp>
Step #3: On the Windows PC, start UFM to run the Workflow:
./ufm.sh ufm_zip_enc_ftp.xml
UFM will start, compress the selected directories, encrypt the compressed files and then upload the files to a remote server.
The last item is to create a Window’s Task Scheduler entry and have the UFM Workflow run everyday at a particular time.
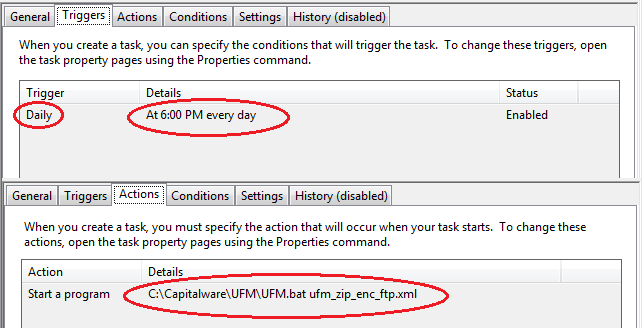
This blog demonstrates how easy it is to backup selected directories to a remote server. Hopefully, this will motive people to do daily backups of their important files.
Regards,
Roger Lacroix
Capitalware Inc.
WebSphere MQ Development, IBM United Kingdom Laboratories has released version 7.5 of SupportPac MO72.
http://www.ibm.com/support/docview.wss?uid=swg24007769
SupportPac MO72 is a command line tool for issuing MQSC commands to a queue manager or client.
Regards,
Roger Lacroix
Capitalware Inc.
Mozilla Firefox has just released Mozilla Firefox v26.0.
http://www.mozilla.com/firefox/
Mozilla Firefox is a free and open source web browser descended from the Mozilla Application Suite and managed by Mozilla Corporation. To display web pages, Firefox uses the Gecko layout engine, which implements most current web standards in addition to several features that are intended to anticipate likely additions to the standards
Regards,
Roger Lacroix
Capitalware Inc.
Over the weekend, I read Alan Zeichick’s article Protect your developer data and it made me smile as I’ve been through the exact same thing many times over the years. Of course, it made me think, are people/companies backing up their data or just flying by the seat of their pants. Do people think that ‘backing up their data is something they may do someday but not today’?
For me, I can’t take any chances, as my life exists in the digital world (so to speak) and I could never ever afford/tolerate any data loss. I have put tens of thousands of hours into creating software products (commercial & open source), documentation, tutorials, web sites, etc. and I couldn’t simply recreate it without a whole lot of work, if some or all of it disappeared (actually, it would be devastating). So, I’m a little anal about backing up my data. 🙂
A little history on my desktop PC step up – its a little different, kind of like me. Back in the 90’s. I used to have my PC setup to triple boot (OS/2, Windows and Linux). So, to be able to get access to my programs or documents, I had to separate my files from the OSes. I created a separate partition for each OS and created other partitions to hold programs and documents. Over time, I found it easier to have separate PCs to run OS/2 (I don’t use OS/2 any more), Windows and Linux and use VNC or telnet to them and do what I need to do but the partitioning on my desktop PC stuck plus I have had the ‘blue screen of death’ too many times to actually trust Windows!!
So, here’s how I partition the hard drives on my desktop PC:
If you are curious how I do the partitioning from a hardware perspective, I have 2 SSD (Solid State Drive) drives in my desktop PC. The first SSD is partitioned as C and G Drives and the second SSD is partitioned as D, E and F Drives. Why like that, well, I’ll tell you. The 2 most heavily used partitions are C (Windows OS) and D (all of the applications) drives, so I wanted them on separate physical drives. Hence, I will get the best throughput with this configuration. Also, the G Drive is rarely used, so it made sense to pair it with the C Drive partition. So, that’s the why!!
Also, the reason I still keep nothing on the C Drive except for Windows is because (roughly) 5 years ago, I got the ‘blue screen of death’ (running WinXP) and Windows would not start except in bare bones ‘safe mode’. I tried to repair it, searched on the internet (with another PC) for a solution but in the end, I formatted the C drive and re-installed Windows. Hence, if I had any data on the C drive, I would have lost it. So, keeping my data on a separate partition is well worth the 1 minute of time to create the separate partition.
So, back to Alan Zeichick’s article. One of the backup procedures (more on this in a minute) that I use is to do daily and weekly backups to my NAS (Network Attached Storage). After a lot of research, the first NAS I purchased was a Buffalo TeraStation Terabyte (1TB) NAS back in 2005. It had 4 256GB drives in it for a total 1TB. I setup it up as RAID-5 which meant I got roughly 750GB of storage which was fine for my needs back then. It ran fine for several years and then one day I got the ‘red blinking light’. Since, this was new to me, I freaked-out. After I realized that my data was still safe, I followed the procedure and replaced the bad drive. I ran the reconfigure option and a few hours later, the red light was gone and everything was bad to normal.
In 2009 (or 2010, I can’t remember), I got another ‘red blinking light’ on the nearly full NAS. I thought, I could replace the 256GB hard drive or simply get a new Buffalo TeraStation III 4TB NAS. I opted for the new NAS, sense the old one was nearly full. I configured the new NAS in a RAID-5 configuration and copied everything from the old NAS to the new NAS.
A couple of months ago (in 2013), I got the ‘red blinking light’ on the 4TB NAS, so I searched around looking for a replacement 1TB drive and found that Best Buy happen to be dumping Seagate Barracuda 1TB drives for $74.99, so I bought 4. Yes, I only needed one, but the price was excellent and they may be hard to find in the future. So it seemed logical to me to stock up now. I put them on the shelf right next to the NAS. So, the next time I see a ‘red blinking light’, I’ll just grab one of the new drives, pop-out the dead drive and put in the brand new drive. Oh, I forgot to mention, the NAS supports hot-swappable drives, which means you don’t have to turn it off to swap out the drives – very cool!!
Besides using the NAS as a backup device, I create ‘shared folders’ on it. I have a ‘music’ share on it where I put all of my converted CDs (yes, I still buy CDs). The ‘music’ share has a little over 11,000 songs on it. Hence, no matter what computer I am using (i.e. Windows, Mac or Linux), I can access the ‘music’ share.
Now back to my anal backup procedures (you’ll see in a minute why I describe it that way). There are 2 pieces of backup software that I rely on: Cobian Backup and Robocopy.
So, those are my backup procedures that I have setup. Is it complete? I think I have covered off 99.999% of the situations that could occur to cause data loss. Is it a little over the top? Probably. But better safe than sorry. 🙂
If you don’t backup your data, please take a moment and implement a solution. You don’t have to do what I do, as there are plenty of easy solutions like external backup hard drives. For those people who use digital cameras or take pictures on your phone, what would you do if you lost ALL of your pictures because your hard drive crashed or your PC was stolen?
Food for thought.
Regards,
Roger Lacroix
Capitalware Inc.
There have been a lot of discussions recently about NSA snooping on data traffic between servers. Microsoft has been extremely quiet and evasive about where in the transfer the data is unencrypted between Microsoft Servers.
A couple of weeks ago, Ars Technica had the following article where Microsoft’s Dorothee Belz, EMEA VP for Legal and Corporate Affairs, said “Generally, what I can say today is server-to-server transportation is generally not encrypted. This is why we are currently reviewing our security system.”
Yesterday (November 5th, 2013), Slashdot posted an article called Microsoft’s NSA ‘Transparency’ Push Remains Pretty Opaque. So far, nothing has changed.
So, what does this have to do with Capitalware’s MQAUSX product? Well, it goes like this: If a customer installs the MQAUSX on a Windows 2003/2008/2012 Server and the MQAdmin sets the authentication target as Microsoft’s Active Directory, is there a security exposure of the user credentials?
Why am I concerned? When customers purchase MQAUSX and implement the MQAUSX client-side security exit, they expect that the user credentials will remain encrypted for the entire communication process. But with Microsoft’s silence on this issue, customers who use MQAUSX on a Windows Server, do not know what to expect when MQAUSX issues a Windows API call to perform authentication against Active Directory. Is the data traffic (UserID and Password) between Windows Server and Active Directory encrypted or unencrypted? That’s my $64,000 question.
If NSA is snooping on data traffic then that would be one of the best places to snoop.
Therefore, until we know for sure or Microsoft issues a public statement that the data traffic is encrypted between Windows Server and Active Directory (or issues a patch), Capitalware recommends that customers switch to an authentication format that is encrypted. Since Active Directory supports LDAP V3 style authentication, Capitalware recommends using LDAP over SSL connection to Active Directory. By doing this, no one can snoop at the user credentials as they are passed from a Windows Server to Active Directory.
Regards,
Roger Lacroix
Capitalware Inc.
D. Richard Hipp has just released SQLite v3.8.2.
http://www.sqlite.org/news.html
SQLite is a software library that implements a self-contained, serverless, zero-configuration, transactional SQL database engine. SQLite is the most widely deployed SQL database engine in the world. The source code for SQLite is in the public domain.
Regards,
Roger Lacroix
Capitalware Inc.
 IBM MQ WebSphere MQ IBM Developer Messaging Blog T.Rob’s Store and Forward Mark Taylor’s Blog Lyns Random Thoughts Leif Davidsen’s Blog Colin Paice on MQ StackOverflow MQ Questions StackOverflow MQTT Questions